Which ISO standards does Orisynx support?
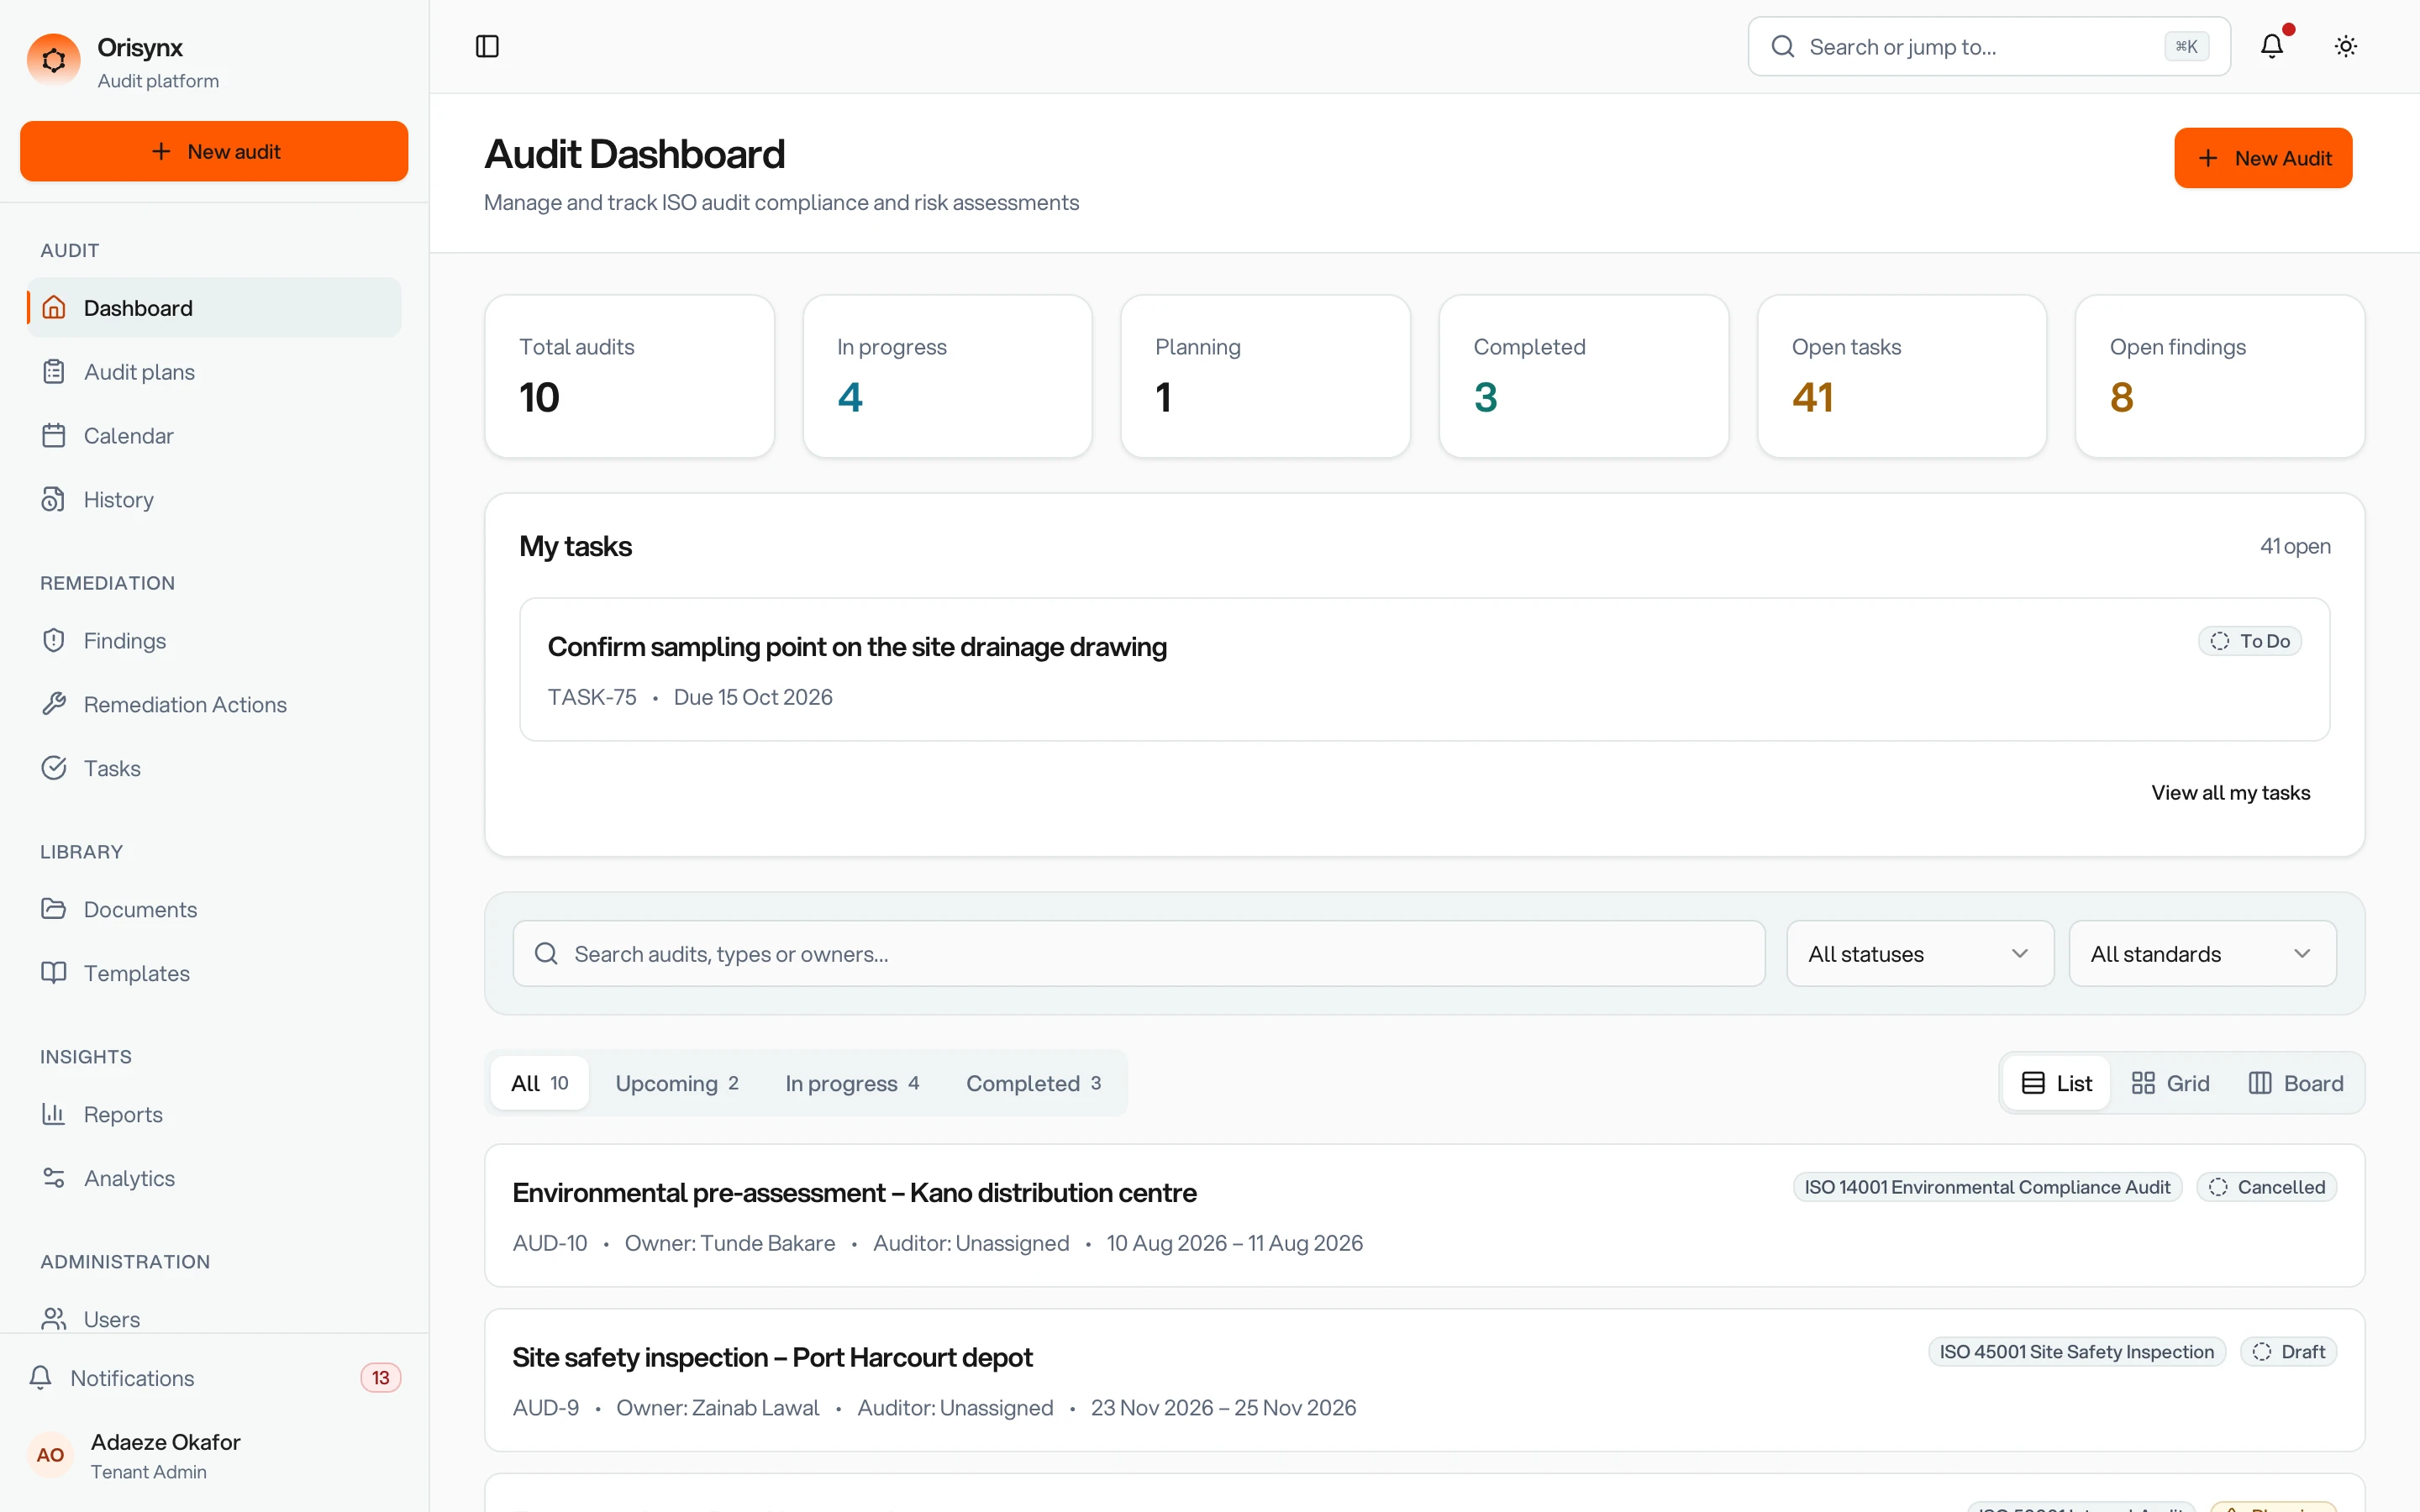
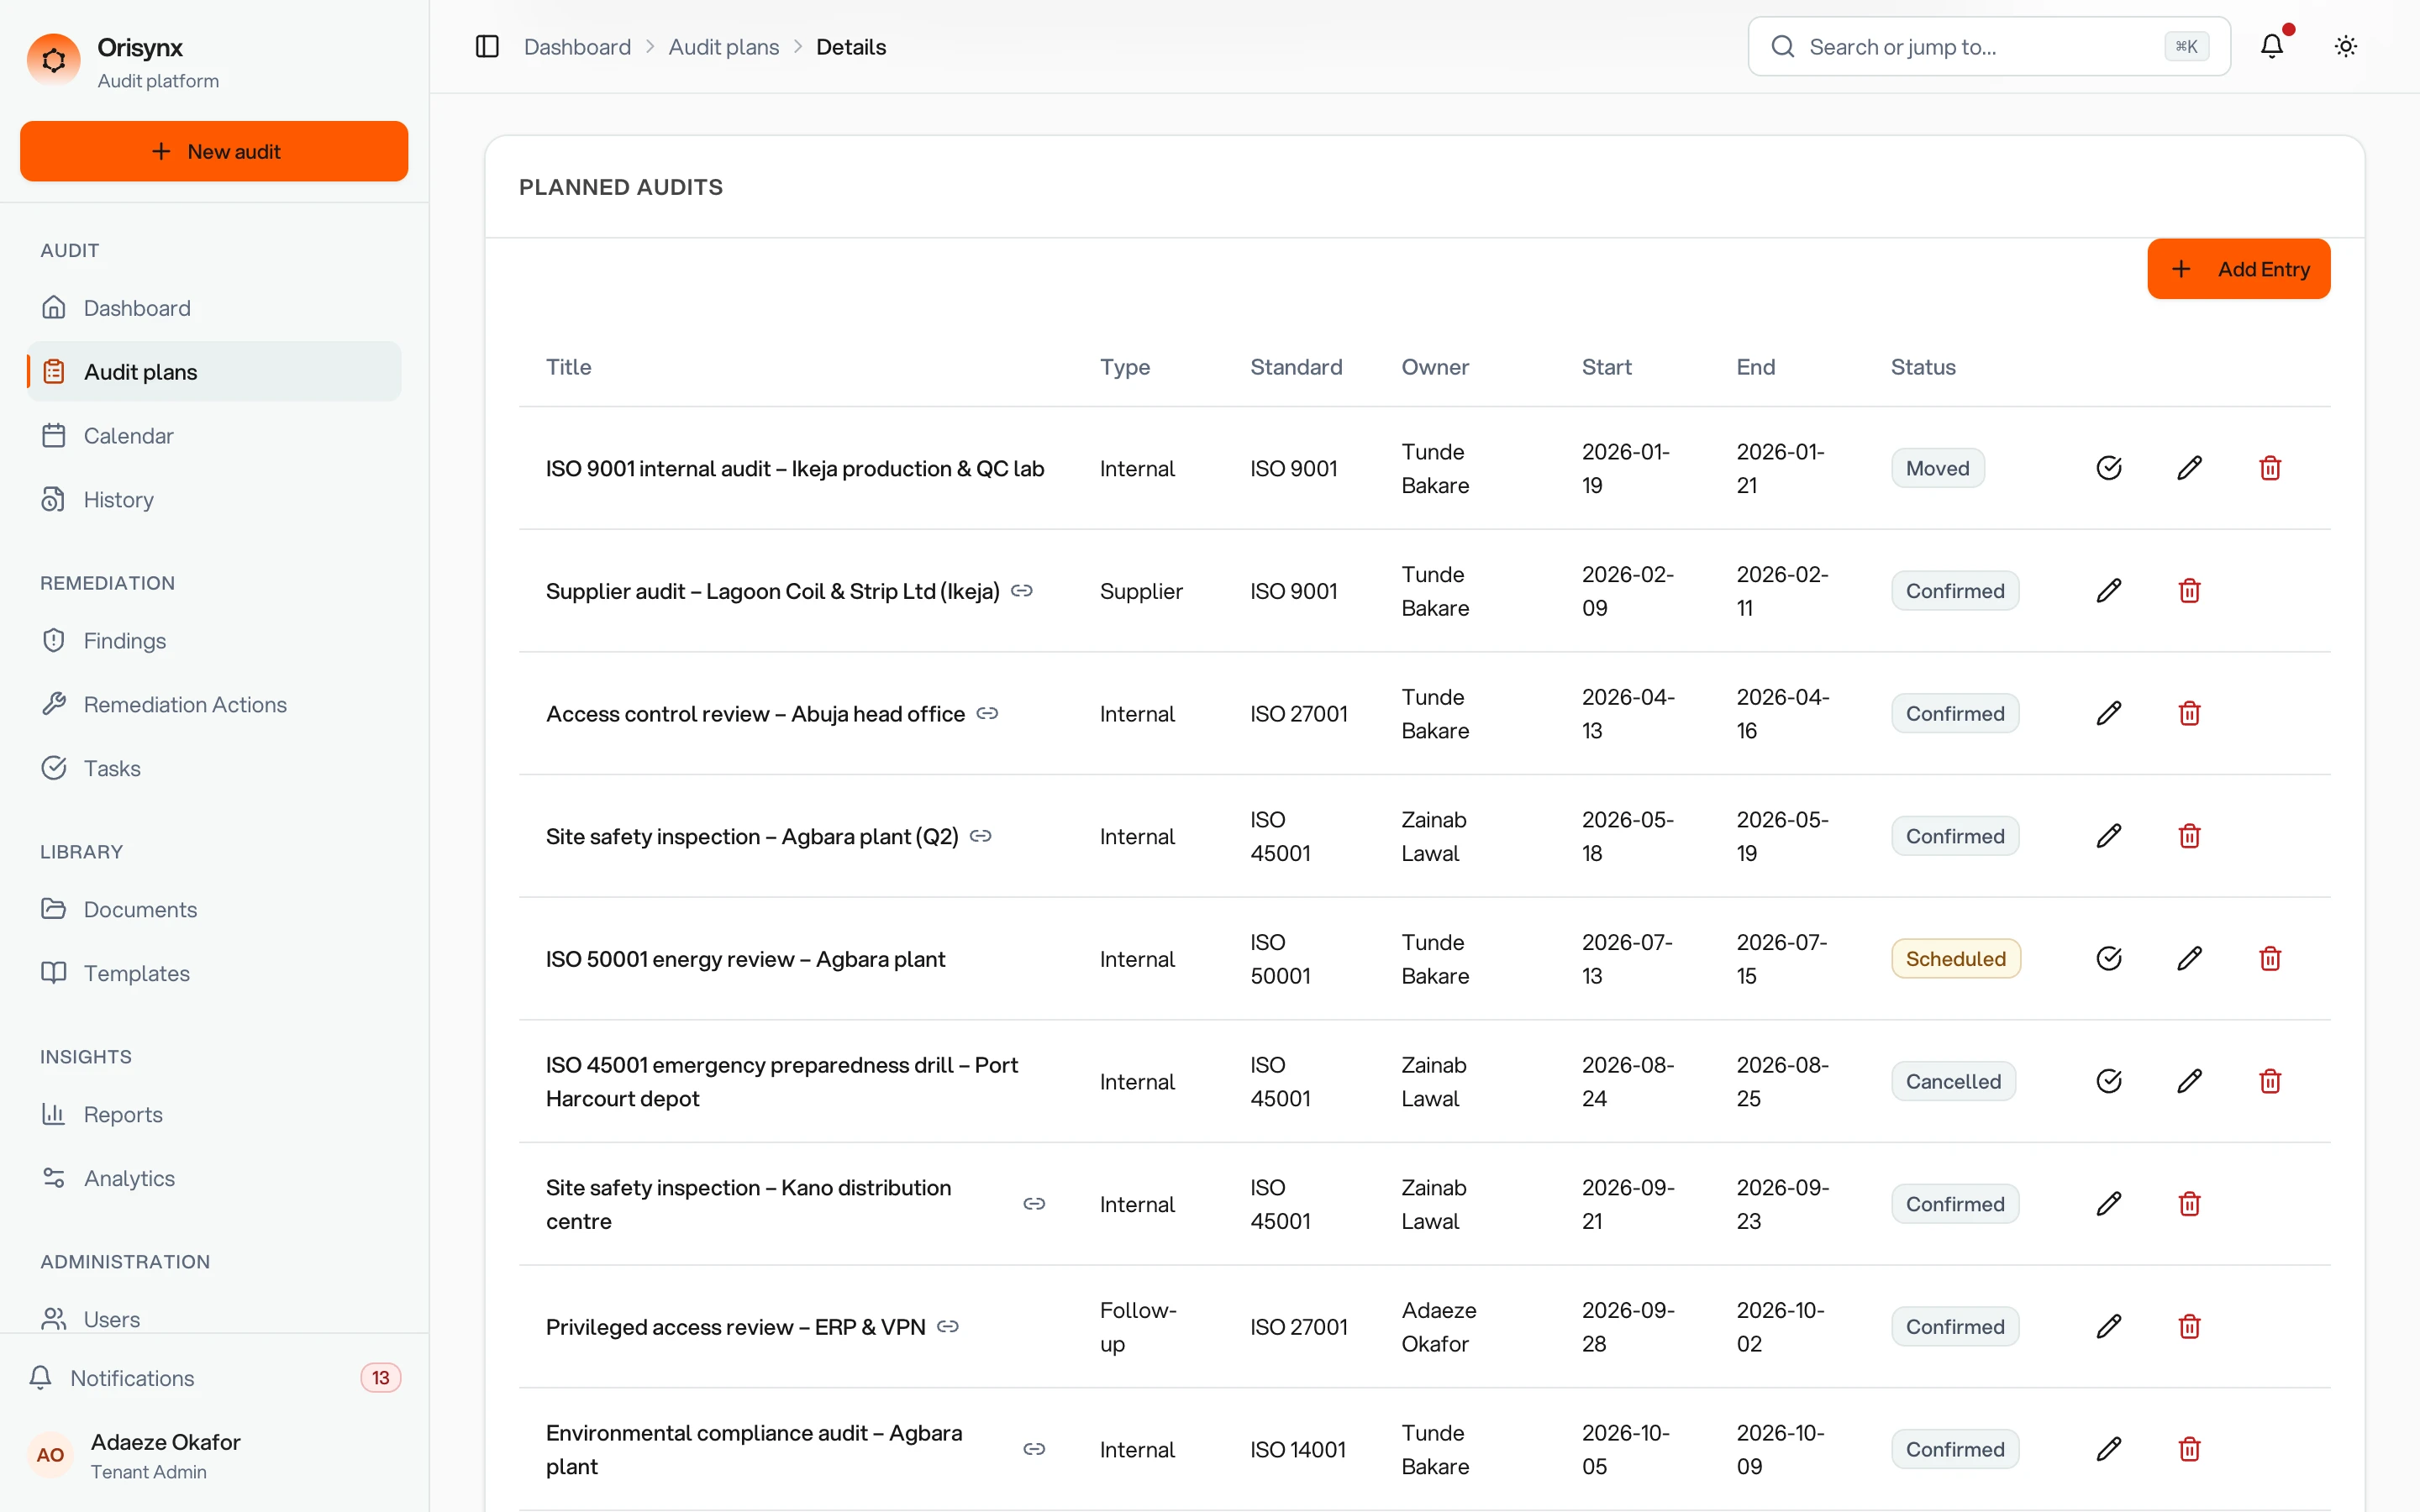
Audits and audit plans can be set against ISO 9001, ISO 14001, ISO 27001, ISO 45001 and ISO 50001. For anything else, such as an internal policy, a customer requirement or another framework, build your own template.
Can we bring our existing audit programme across?
Yes. Import a whole programme from an .xlsx or .csv file. Orisynx checks every row before anything is created and tells you exactly which cells need fixing.
Does Orisynx handle corrective actions as well as findings?
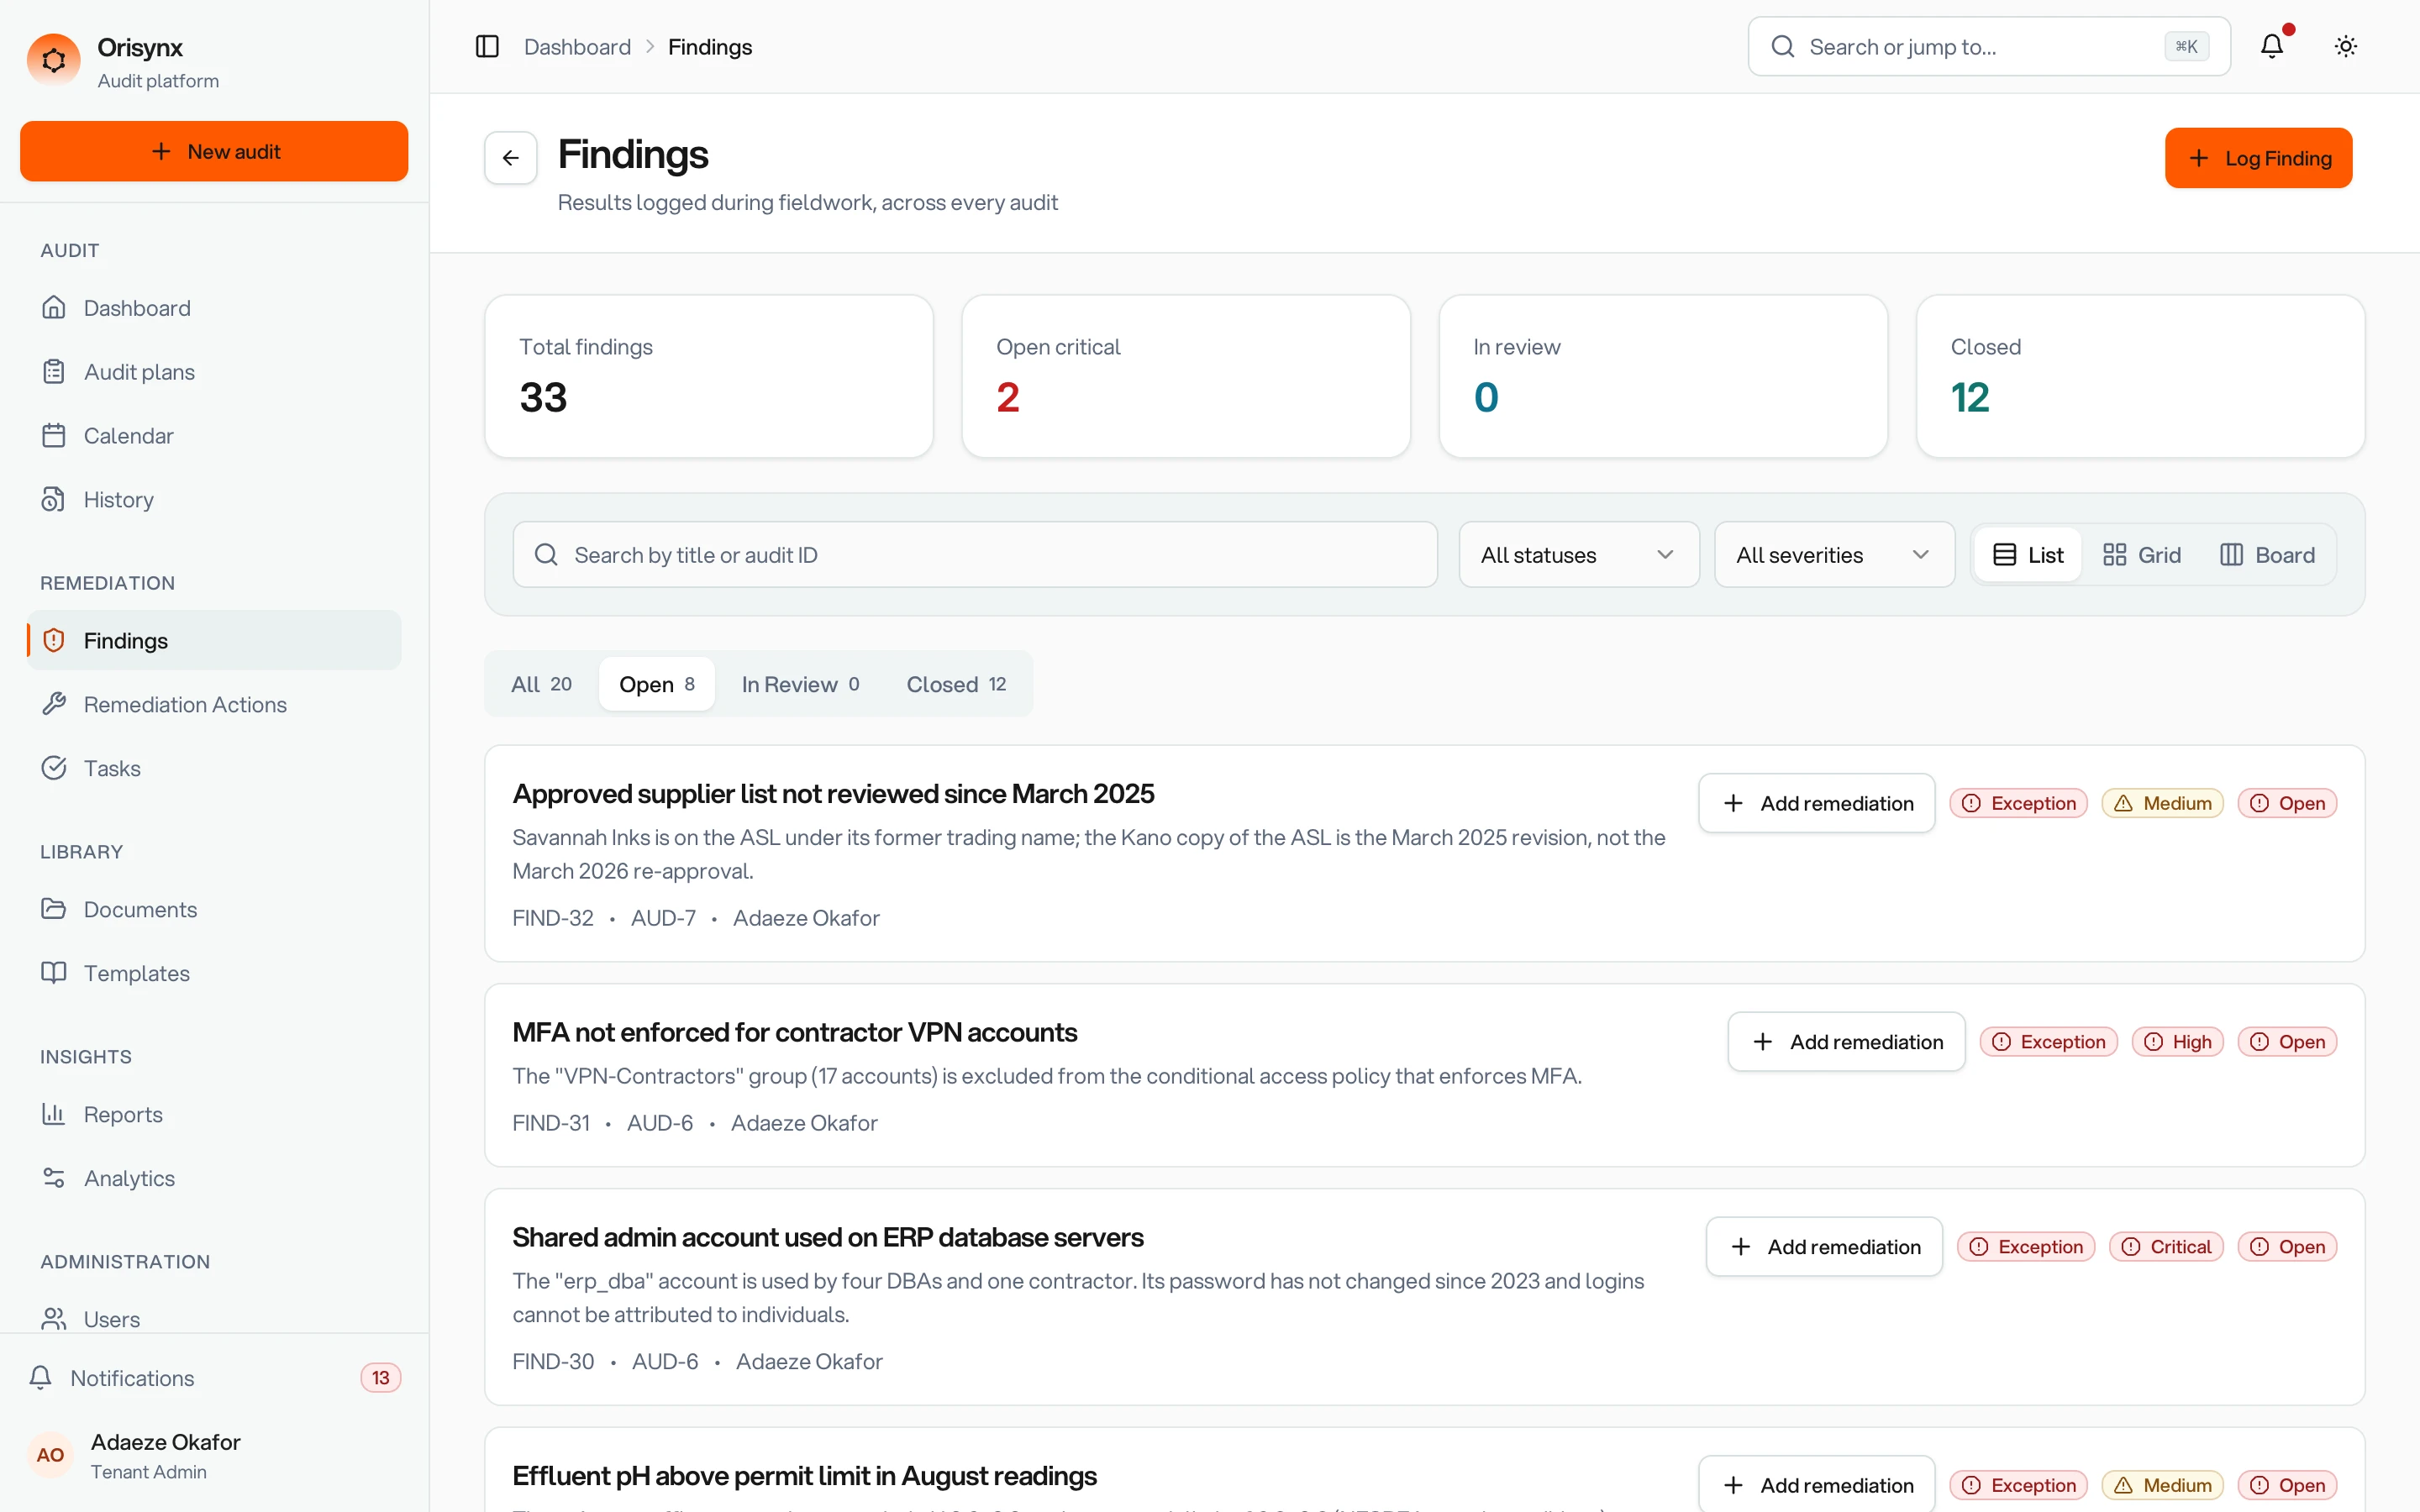
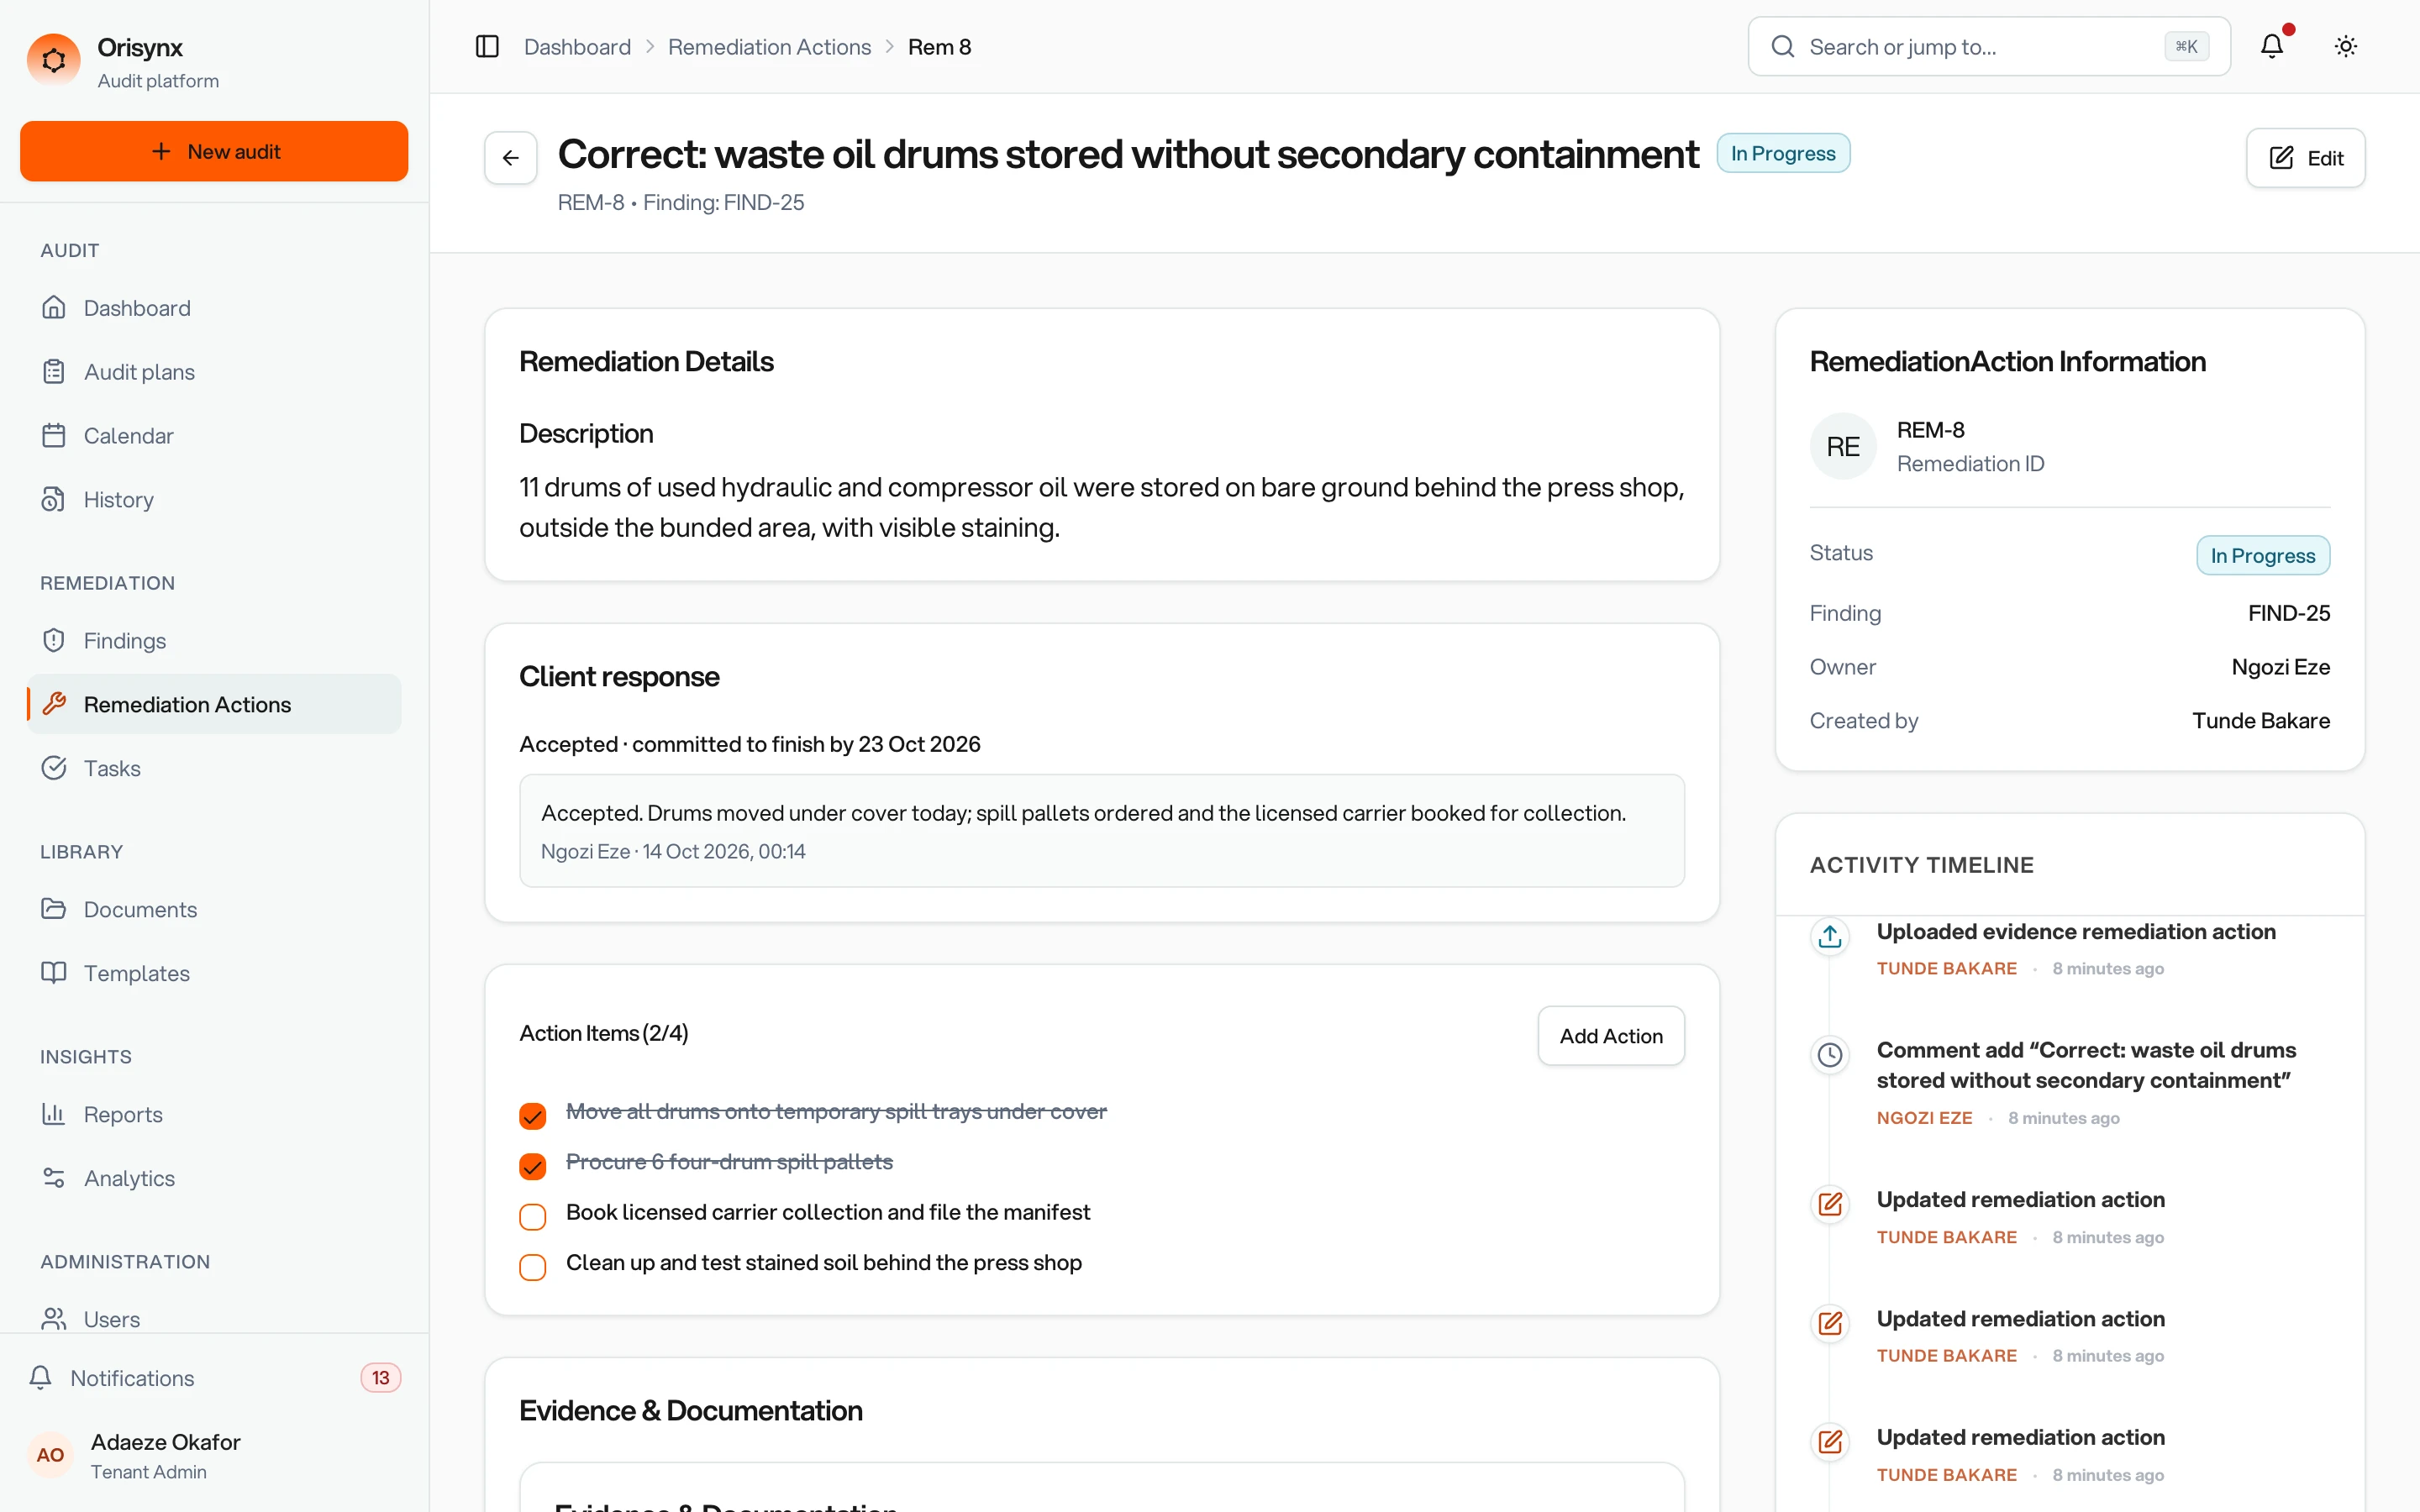
Every finding can carry corrective and preventive actions with an owner, a due date and tasks. The owner accepts or disputes the action, works it through to verification, and a reviewer records whether it was effective.
What kinds of audit can we run?
Internal, external, supplier, surveillance, certification and follow-up audits, all in the same programme and calendar.
Who can see and change what?
Access is set by role and permission, and people can be organized into groups. Auditors, auditees and managers each see the work that is theirs.
Is our data kept apart from other organizations?
Each organization gets its own workspace backed by its own database. Read more on the security page.
How do people know what is due?
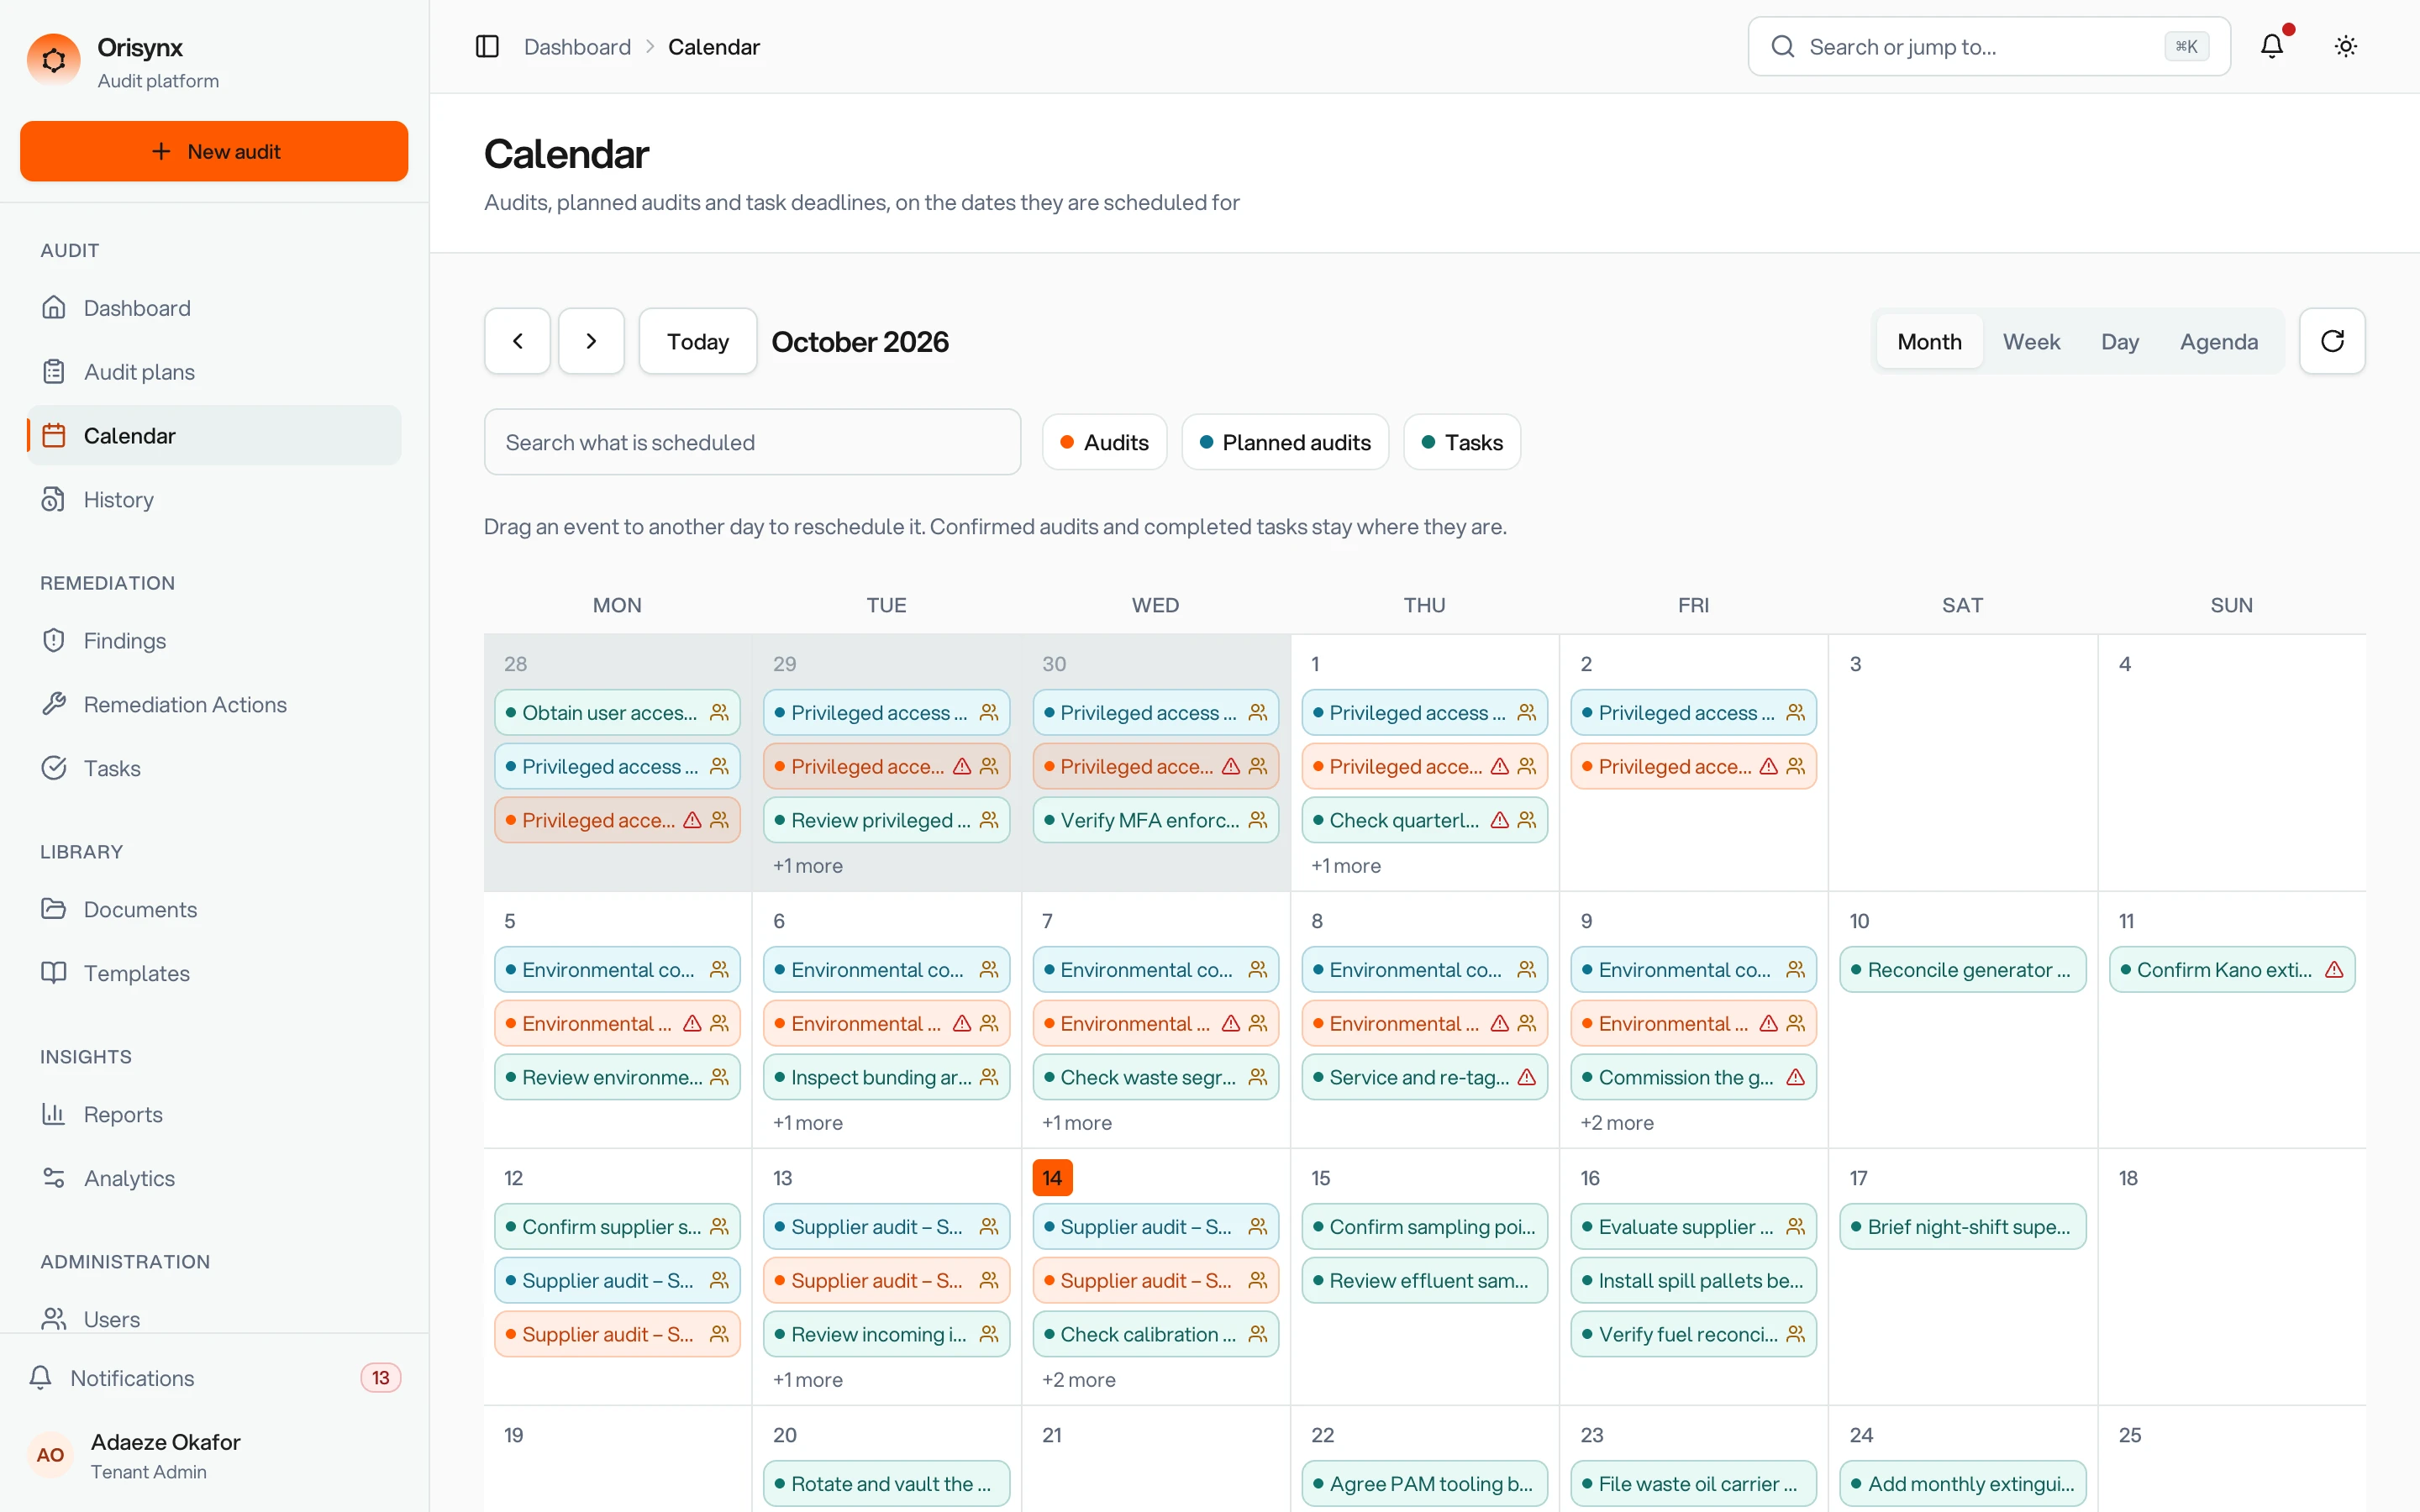
In-app notifications flag new work as it is assigned, the shared calendar shows audits and due dates, and each person gets a daily email digest of anything overdue or due soon.
Can we run one programme across several states?
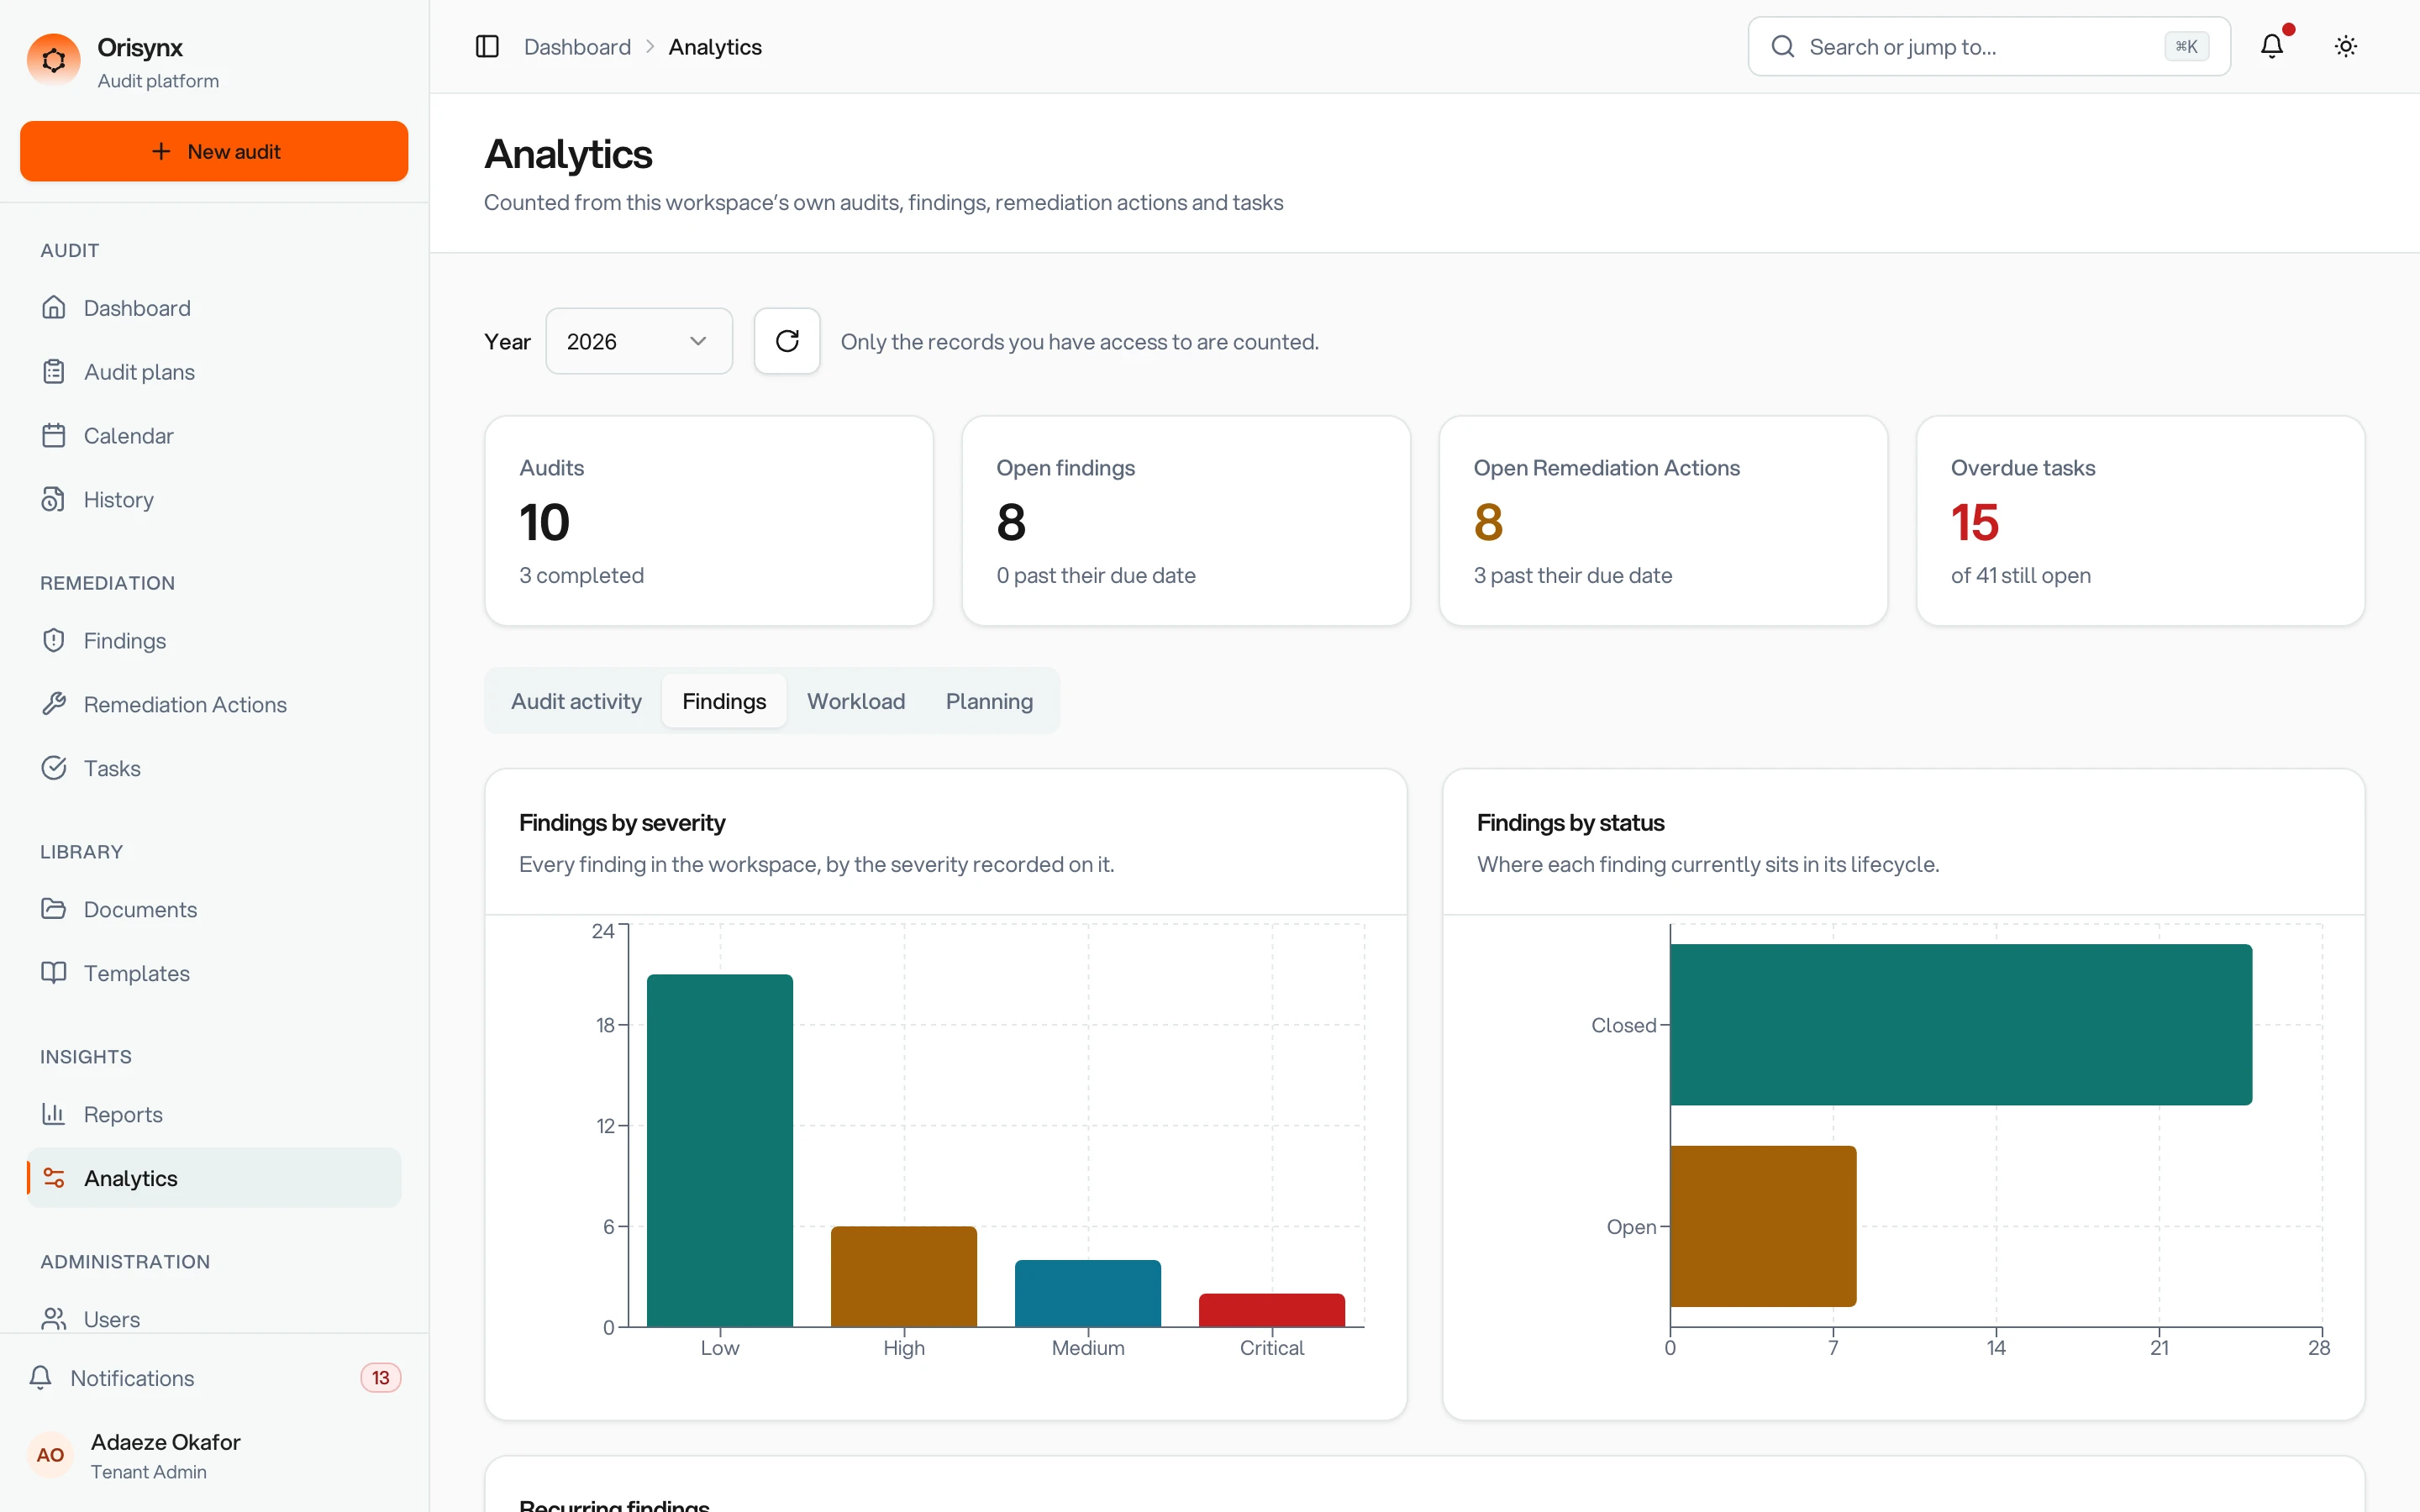
Yes. Every planned audit belongs to a department or site, so a head office in Abuja, plants in Ogun and depots in Rivers can share one programme, with progress shown for each.
How do we get started?
Book a demo. We set up a workspace for your organization and you invite your team by email.